At Deloitte, we work on the technology that keeps the UK secure, resilient, and ready for tomorrow. Our Defense & Security engineers build the digital foundations behind some of the most complex systems in government – from critical infrastructure to advanced data platforms. We don’t just test code – we test products that matter. As an SDET here, you’ll apply engineering discipline to drive quality – building automation frameworks that scale, crafting solutions that find defects fast to accelerate delivery, and helping our clients build confidence in what they deploy. We’re growing rapidly across our Defense & Security portfolio. If you already hold DV clearance and want to design, build, and test solutions that protect the nation, we’d love to meet you. Connect to your career at Deloitte Deloitte drives progress. Using our vast range of expertise, we help our clients' become leaders wherever they choose to compete. To do this, we invest in outstanding people. We build teams of future thinkers, with diverse talents and backgrounds, and empower them all to reach for and achieve more. What brings us all together at Deloitte? It’s how we approach the thousands of decisions we make every day. How we behave, our beliefs and our attitudes. In other words: our values. Whatever we do, wherever we are in the world, we lead the way, serve with integrity, take care of each other, foster inclusion, and collaborate for measurable impact. These five shared values lead every decision we make and action we take, guiding us to deliver impact how and where it matters most. Connect to your opportunity This team is focused on the technical delivery of new solutions that solve complex challenges for clients. Join us to drive innovation and technology forward, collaborating with cross-functional teams and using cutting-edge tools. Offering excellent development opportunities, you will have the chance to hone your technical craft, gain new skills, and complete qualifications and certificates. This is your chance to make a real impact. We’re looking for test engineers who love writing code and finding bugs. As an SDET, you’ll build automation frameworks that form the backbone of modern delivery. You’ll help clients deliver faster, with confidence, across some of the largest and most technically ambitious programmes in the country. You’ll work shoulder-shoulder with developers, DevOps engineers, and business analysts – designing, implementing, and scaling test automation that works I the real world. You’ll be trusted to make technical decisions, explore and implement new tools, and shape how our teams delivery quality. You might find yourself: Designing and implementing modern test automation frameworks for APIs, microservices, and front-end applications. Embedding test automation in CI/CD pipelines using tools such as, Azure DevOps, Jenkins, or GitHub Actions. Writing maintainable, readable tests in languages such as Java, Python, C, or JavaScript/TypeScript. Collaborating with client and Deloitte teams to define the right approach to quality across projects. Analysing failures, identifying root causes, and improving test reliability. Mentoring others and contributing to Deloitte’s internal tools, accelerators, and communities of practice. Your work will have national impact – the systems we test are used by millions of people every day, often in mission-critical environments. Connect to your skills and professional experience You’re curious, collaborative, and hands-on. You care about clean, testable code. You take initiative and are pragmatic – you know when to automate, when to refactor, and when to ship. You bring clarity to complexity with great communication and enjoy helping teams build confidence through quality engineering. Essentials: UK Developed Vetting (DV) clearance Strong coding skills in at least one of: Java, C, Python, or JavaScript / TypeScript Experience building or extending automation frameworks (API, web, or mobile) Familiarity with testing frameworks and tools, such as Selenium, RestAssured, Appium, Cucumber, or Playwright Experience with source control, such as Git Experience working in agile teams, using tools such as Jira, or Azure DevOps A collaborative mindset and strong communication skills Desirables: Practical knowledge of CI/CD pipelines Understanding microservice and container-based architectures Experience with cloud technologies (AWS, Azure, or GCP) Contributions to open-source projects or developer communities Knowledge of performance, security, or accessibility testing Exposure to infrastructure-as-code or container orchestration tools (Docker, Kubernetes, Terraform) Connect to your business - Technology and Transformation Distinctive thinking, deep expertise, innovation and collaborative working. That’s what connects us. That’s what makes us Deloitte. If you want to help solve some of the biggest tech and transformational challenges around, join us. Together, we’ll make an impact that matters. Engineering, AI and Data We lead transformation at the heart of our clients; re-engineering the core of our clients’ organisations, helping to unleash growth, and creating better futures for their customers, citizens and employees. Personal independence Regulation and controls are standard practice in our industry and Deloitte is no exception. These controls provide important legal protection for both you and the firm. We are subject to a number of audit regulations, one of which requires that certain colleagues abide by specific personal independence constraints (e.g., in relation to any financial interests and employment relationships). This can mean that you and your "Immediate Family Members" are not permitted to hold certain financial interests (shares, funds, bonds etc.) with audit clients of the firm, and also prohibitions on certain employment relationships (e.g., you are not permitted to hold a secondary employment role with SEC audit clients of the firm whilst being employed by the firm). The recruitment team will provide further detail as you progress through the recruitment process or you can contact the Independence team upon request. Connect with your colleagues “What attracted me to Deloitte were the endless opportunities and the collective experience of other like-minded individuals. Deloitte’s clients include many of the world’s largest organisations; I wanted to be part of a team that made a difference that I could be proud of.” - Dan, Technology and Transformation Our hybrid working policy You’ll be based in Bristol or Manchester with hybrid working. At Deloitte we understand the importance of balancing your career alongside your home life. That’s why we’ll support you to work flexibly through our hybrid working policy. Depending on the requirements of your role, you’ll have the opportunity to work in your local office, virtual collaboration spaces, client sites and remotely. You’ll get the chance to meet face to face when needed, while you collaborate and learn from colleagues, share your experiences, and build the relationships that will fuel your career and prioritise your wellbeing. Please check with your recruiter for the specific working requirements that may apply for your role. Our commitment to you Making an impact is more than just what we do: it’s why we’re here. So we work hard to create an environment where you can experience a purpose you believe in, the freedom to be you, and the capacity to go further than ever before. We want you. The true you. Your own strengths, perspective and personality. So we’re nurturing a culture where everyone belongs, feels supported and heard, and is empowered to make a valuable, personal contribution. You can be sure we’ll take your wellbeing seriously, too. Because it’s only when you’re comfortable and at your best that you can make the kind of impact you, and we, live for. Your expertise is our capability, so we’ll make sure it never stops growing. Whether it’s from the complex work you do, or the people you collaborate with, you’ll learn every day. Through world-class development, you’ll gain invaluable technical and personal skills. Whatever your level, you’ll learn how to lead. Connect to your next step A career at Deloitte is an opportunity to develop in any direction you choose. Join us and you’ll experience a purpose you can believe in and an impact you can see. You’ll be free to bring your true self to work every day. And you’ll never stop growing, whatever your level. Discover more reasons to connect with us, our people and purpose-driven culture at deloitte.co.uk/careers
Job listings
Cyber security visa sponsorship jobs in the UK
Jobs at employers on the Home Office register of licensed sponsors. Confirm sponsorship with the employer for each role.
6 jobs
Do you want to be at the heart of some of the biggest and most ambitious programmes undertaken to keep our country safe? We are proud of the impact we have with our Defence & Security clients, the strength of our relationships, and the variety of our skills and expertise that we bring to help them achieve their mission. We’re growing our teams across all of Technology and Transformation. If you are cleared DV level, we are very keen to hear from you. Connect to your career at Deloitte Deloitte drives progress. Using our vast range of expertise, we help our clients become leaders wherever they choose to compete. To do this, we invest in outstanding people. We build teams of future thinkers, with diverse talents and backgrounds, and empower them all to reach for and achieve more. What brings us all together at Deloitte? It’s how we approach the thousands of decisions we make every day. How we behave, our beliefs and our attitudes. In other words: our values. Whatever we do, wherever we are in the world, we lead the way, serve with integrity, take care of each other, foster inclusion, and collaborate for measurable impact. These five shared values lead every decision we make and action we take, guiding us to deliver impact how and where it matters most. Connect to your opportunity This team is focused on the technical delivery of new solutions that solve complex challenges for clients. Join us to drive innovation and technology forward, collaborating with cross-functional teams and using cutting-edge tools. Offering excellent development opportunities, you will have the chance to hone your technical craft, gain new skills, and complete qualifications and certificates. This is your chance to make a real impact. We're looking for people who are, by which we mean natural initiative-takers who bring out the best in others, are brilliant listeners and can grow our business without compromising standards, integrity or culture. We are seeking a highly skilled and motivated Full Stack Developer to join our dynamic team in the public sector. The ideal candidate will possess a strong background in both front-end and back-end development, with a focus on creating innovative and efficient solutions for government-related projects. The successful candidate will play a key role in designing, implementing, and maintaining web applications that address the unique challenges and requirements of Defence & Security. Design, develop, and deploy robust web applications for public sector projects. Contribute to the entire software development lifecycle in collaboration with cross-functional teams. Create responsive user interfaces using modern front-end technologies and frameworks. Develop secure and efficient server-side logic, utilizing languages and frameworks. Implement security best practices, ensuring compliance with government regulations. Conduct regular security assessments and collaborate to address vulnerabilities. Develop and maintain well-documented RESTful APIs for seamless system communication. Work with project managers, UX/UI designers, and stakeholders to translate requirements into technical specifications. Communicate effectively with non-technical stakeholders for feedback and alignment with project goals. Connect to your skills and professional experience All applicants must hold (or willing to be security cleared) UK security clearance to Developed Vetting level. Candidates will have hands-on experience with one or more technologies (or equivalent) relevant to these areas: Essentials skills: Proficient in modern front-end technologies: HTML5, CSS3, JavaScript, and frameworks like React, Angular, or Vue.js. Strong skills in server-side logic using languages such as Node.js, Python, or Java. Experience with both SQL and NoSQL databases, including data modelling for government applications. Proficient in analyzing complex issues and implementing effective solutions for public sector challenges. Flexibility to navigate changing project requirements in the dynamic public sector environment. Strong verbal and written communication skills to convey technical concepts; ability to collaborate effectively in cross-functional teams. Desirable skills: Familiarity with government processes, policies, and systems, enhancing the ability to tailor solutions to public sector needs. Understanding of UX principles to create applications that are accessible and user-friendly for government officials and the public. Proven ability to develop and maintain well-documented RESTful APIs for seamless system communication. Experience with implementing and adhering to security best practices for government data. Connect to your business - Technology and Transformation Distinctive thinking, deep expertise, innovation and collaborative working. That’s what connects us. That’s what makes us Deloitte. If you want to help solve some of the biggest tech and transformational challenges around, join us. Together, we’ll make an impact that matters. Customer Human connections are integral to business. We combine people, ideas and technology to support our clients to build strong connections. For example, through commerce, customer design and sales services. Personal independence Regulation and controls are standard practice in our industry and Deloitte is no exception. These controls provide important legal protection for both you and the firm. We are subject to a number of audit regulations, one of which requires that certain colleagues abide by specific personal independence constraints (e.g., in relation to any financial interests and employment relationships). This can mean that you and your "Immediate Family Members" are not permitted to hold certain financial interests (shares, funds, bonds etc.) with audit clients of the firm, and also prohibitions on certain employment relationships (e.g., you are not permitted to hold a secondary employment role with SEC audit clients of the firm whilst being employed by the firm). The recruitment team will provide further detail as you progress through the recruitment process or you can contact the Independence team upon request. Connect with your colleagues “What attracted me to Deloitte were the endless opportunities and the collective experience of other like-minded individuals. Deloitte’s clients include many of the world’s largest organisations; I wanted to be part of a team that made a difference that I could be proud of." - Dan, Technology and Transformation Our hybrid working policy You’ll be based in Bristol, Cambridge, London, or Manchester with hybrid working. At Deloitte we understand the importance of balancing your career alongside your home life. That’s why we’ll support you to work flexibly through our hybrid working policy. Depending on the requirements of your role, you’ll have the opportunity to work in your local office, virtual collaboration spaces, client sites and remotely. You’ll get the chance to meet face to face when needed, while you collaborate and learn from colleagues, share your experiences, and build the relationships that will fuel your career and prioritise your wellbeing. Please check with your recruiter for the specific working requirements that may apply for your role. Our commitment to you Making an impact is more than just what we do: it’s why we’re here. So we work hard to create an environment where you can experience a purpose you believe in, the freedom to be you, and the capacity to go further than ever before. We want you. The true you. Your own strengths, perspective and personality. So we’re nurturing a culture where everyone belongs, feels supported and heard, and is empowered to make a valuable, personal contribution. You can be sure we’ll take your wellbeing seriously, too. Because it’s only when you’re comfortable and at your best that you can make the kind of impact you, and we, live for. Your expertise is our capability, so we’ll make sure it never stops growing. Whether it’s from the complex work you do, or the people you collaborate with, you’ll learn every day. Through world-class development, you’ll gain invaluable technical and personal skills. Whatever your level, you’ll learn how to lead. Connect to your next step A career at Deloitte is an opportunity to develop in any direction you choose. Join us and you’ll experience a purpose you can believe in and an impact you can see. You’ll be free to bring your true self to work every day. And you’ll never stop growing, whatever your level. Discover more reasons to connect with us, our people and purpose-driven culture at deloitte.co.uk/careers
Do you want to apply data science to one of the most important challenges in health research: enabling safe use of sensitive data at scale? In this role, you’ll develop privacy and security controls that protect participants while helping researchers generate insights faster and more safely. Our Future Health is an ambitious collaboration between the public, charity and private sectors, designed to help people live healthier lives for longer through better prevention, earlier detection and improved treatment of diseases. We will speed up the discovery of new methods of early disease detection, and the evaluation of new diagnostic tools, to help identify and treat diseases early, when outcomes are usually better. With over 2.5M volunteers across the UK, we’re now the world’s biggest health research programme of its kind, and our volunteer group is also more diverse than other, similar health research programmes. Technology and data are central to our mission. Our systems power web sites, clinics across the UK, secure analytics and research systems, pipelines that process highly sensitive health and genetic data, and we are continuing to grow our data science capability to support this ambition. To realise our ambition safely, we need to continue developing world-class approaches to data privacy, data security and responsible access to health data. We are looking for a Senior Data Scientist specialising in privacy, security and risk modelling, to help design, build and scale data-driven controls that protect participants while enabling cutting-edge research. This is a hands-on role where you’ll apply strong data science skills and an engineering mindset to real operational problems: safe outputs review, re-identification risk, privacy risks in trained models, synthetic data, and data-driven security controls. You will work closely with teams across Product, Security, Engineering, Science, Data Protection, and Researcher Operations as well as external experts to develop practical, scalable and evidence-based solutions. You will be expected to work closely with users of these systems including researchers, Airlock reviewers, access governance reviewers and security specialists, to understand their workflows, pain points and risk decisions. A key part of the role will be turning complex privacy and security problems into trusted algorithms, evidence and automated support. What you’ll do Develop data-driven approaches to disclosure control and safe outputs review, supporting the scaling of our TRE (Trusted Research Environment) Airlock. This may include building algorithms and automated review tools to classify outputs, detect potentially disclosive content, identify patterns of risk, and provide explainable decision support for human reviewers. Work directly with Airlock reviewers and operational users to understand where automation can help, where human judgement is essential, and how tools should be designed to support consistent, auditable and proportionate decisions. Contribute to our approach to de-identification and re-identification risk assessment, helping us assess how privacy risk changes across datasets, access models and analytical outputs. Help us develop our approaches to safe AI using health data, including how we assess and manage privacy risks associated with trained models. Explore and develop approaches to synthetic data generation, assessing how synthetic data can be used safely and usefully, and how to evaluate the privacy, fidelity and utility trade-offs of different approaches. Collaborate with our Information Security team on data-driven security control assessment, threat detection and monitoring approaches, including identifying signals of risky behaviour, anomalous activity or misuse of data access environments, and cyber risk quantification. Build prototypes and production-quality code, working with engineers to turn promising approaches into robust, maintainable and auditable tools. Work closely with governance, legal, ethics and operational colleagues to ensure technical controls fulfil their requirements. Keep up with emerging methods in statistical disclosure control, privacy-enhancing technologies, AI security, synthetic data, de-identification and privacy-preserving computation. This role will be fully hybrid with the expectation we get together in our Holborn, London office at least once per month. Requirements We welcome applications from all who may not feel they match the full criteria, so if you have most of the below, we'd like to hear from you: Significant experience applying data science, machine learning, statistical modelling or advanced analytics to complex real-world datasets. Strong applied statistical expertise, including the ability to quantify risk and uncertainty, evaluate assumptions, design validation approaches, interpret imperfect or incomplete evidence, and communicate the limitations of statistical or machine learning models. Strong Python skills and experience writing maintainable, production-quality code. Experience working in cross-functional teams with software engineers, data engineers or platform teams to design and deliver data products, pipelines, analytical services or decision-support tools. A user-focused approach to technical delivery: you are comfortable working with people who operate, review, govern or depend on data systems, and can translate their needs into technical requirements. Applied machine learning experience and understanding of common privacy attacks against data and models, such as memorisation, membership inference, attribute inference, model inversion or leakage through model outputs. Exposure to privacy-preserving machine learning, privacy-enhancing technologies or adjacent research areas (e.g. federated learning, secure aggregation, differential privacy, or confidential computing) Experience working with sensitive, confidential or regulated data and a strong understanding of privacy, confidentiality or information security risks. Ability to translate ambiguous operational, governance or security problems into clear data science questions and practical technical requirements. Good communication skills, with the ability to explain complex technical concepts to non-specialist stakeholders. A pragmatic, delivery-focused mindset It would be a bonus if you have any of the following experience - Working with health data or biomedical research data, electronic health records, and ideally genomic data. Developing models, algorithms or rule-based systems that support human decision-making, ideally where explainability, auditability and risk management are important. Anomaly detection, behavioural analytics, security monitoring or detection engineering. Risk quantification methods from fields such as actuarial science, epidemiology, operational research, or cyber risk. Familiarity with UK data protection, research governance or health data access expectations. Experience with PETs or privacy-preserving ML frameworks such as Flower, Opacus, TensorFlow Federated or similar. Cloud platforms, containerisation, CI/CD, MLOps or production ML systems. Experience evaluating synthetic data using both utility and privacy metrics. Hiring Process We feel hiring should be transparent and give you a real sense for what Our Future Health is like. Here's what you can expect: Initial chat with our Talent team (30 min) to get to know each other, discuss the role, and answer any questions you have. 1st interview with our Head of Data Operations (25 min) - this is an opportunity to meet your potential line manager and for you both to align on role expectations. Technical interview with 2-3 members from our tech and data teams (60 min). This will include a short task you’ll need to prepare in advance of the interview and is designed to get a sense for how you'd approach the real-world responsibilities of this role. Final stage competency interview (60 min) with a small cross-functional panel of your potential new stakeholders. This will focus on how you collaborate, work with stakeholders, and navigate ambiguity and challenges in real-world projects. Benefits Competitive base salary from £80,000 Generous Pension Scheme – We invest in your future with employer contributions of up to 12% 30 Days Holiday pro rata + Bank Holidays – Enjoy a generous holiday allowance with the flexibility to take bank holidays when it suits you Enhanced Parental Leave – Supporting you during life’s biggest moments Cycle to Work Scheme – Save 25-39% on a new bike and accessories through salary sacrifice Home & Tech Savings – Get up to 8% off on IKEA and Currys products, spreading the cost over 12 months through salary sacrifice EV Scheme – Save up to 40% on a brand new electric vehicle all-inclusive package through salary sacrifice £1,000 Employee Referral Bonus – Know someone amazing? Get rewarded for bringing them on board! Wellbeing Support – Access to Mental Health First Aiders, plus 24/7 online GP services and an Employee Assistance Programme for you and your family A Great Place to Work – We have a lovely Central London office in Holborn, and offer flexible and remote working arrangements Join us - let’s prevent disease together. We recommend you apply as soon as possible as occasionally due to high volumes of applications, we need to close our postings early. At Our Future Health, we recognise the importance of having a diverse workforce and ensuring that all candidates, regardless of their background, have equitable access to our application process. We proactively encourage applicants who identify as having a disability, neurodiversity, or long-term health conditions to let us know if they require any reasonable adjustments as part of their application process.
Position: Principal Platform Security Engineer, London Market As a senior and influential member of the London Platform Engineering Chapter, the Principal Platform Security Engineer will set direction and lead by example in maturing our platform security practices. You will guide multiple Innovation squads and Engineering Chapters, driving cloud-first adoption and championing secure-by-design initiatives. You will be an integral member of a Chapter spanning Platform, DevOps, and Site Reliability Engineers, and a core contributor to a Platform Engineering squad focused on continuous improvement across our cloud and on-premises platforms. You will raise engineering standards through automation, reliable design, and pragmatic governance, helping to deliver smarter, more cost-effective, and faster solutions that are reusable across squads. With security embedded across all squads, you will provide visible leadership to strengthen our platform security posture. You will influence priorities, drive the change needed to embed modern DevOps and security ways of working, and ensure teams have the patterns, tooling, and guidance to succeed. As the chapter grows, this role also offers the opportunity to take on people leadership responsibilities, including day-to-day management of third-party security engineers and partner resources. Key Responsibilities Coach and mentor chapter members, and support the Head of Platform Engineering with overall chapter management, particularly across partner resources. Design, implement, and automate security controls and security testing within the SDLC. Lead application security practices, ensuring secure design and build, and coordinate effectively between engineering and security teams. Apply Security-as-Code principles by providing training, creating reusable patterns, and establishing best practices for teams. Support the investigation and future implementation of agentic workflows and agents, ensuring proposed solutions are secure-by-design and comply with Hiscox AI governance. Respond swiftly to new and emerging security threats and vulnerabilities, investigate suspected attacks, and help manage security incidents, including post-incident reviews to identify root causes, implement solutions, and prevent recurrence. Produce clear, actionable security reporting for senior leadership Act as the primary point of contact for security-related inquiries across London Market technology and change initiatives, coordinating with Group, other Business Units, and Cyber teams to advance security practices across Hiscox. Influence key architectural decisions early, balancing business requirements, budgets, security, and resilience. Partner with squads to take solutions from proof of concept (PoC) through to a production-ready platform. Build and maintain secure Azure and GCP infrastructure across all environments using Azure DevOps Pipelines and Terraform. Oversee and coach squads on intra-day deployment mechanisms, advocating for cloud-informed improvements that increase security, reliability, and delivery speed. Build and maintain monitoring and alerting at all levels (infrastructure, application, and data), ensuring actionable signals and secure operational practices. Person Specification : Mandatory skillset: 5+ years’ DevOps/Platform Engineering experience delivering solutions in Azure and/or GCP. Full‑stack application and infrastructure solution design, ensuring robust security controls, high availability, and operational resilience throughout. Working knowledge of vulnerability and compliance management (scanning through to remediation), patch management, endpoint protection/anti-malware, and access control management (e.g., IAM/PAM), including driving findings to closure. Working knowledge of threat modelling and risk assessment, applied to cloud architectures and CI/CD pipelines to guide secure design and prioritised risk treatment. Experience with AppSec tooling, including CI/CD integration, tuning to reduce noise, and triaging results with engineers to prioritise remediation and prevent regressions. Strong leadership skills. You will help lead the wider technology and change teams to improve our DevOps and Security maturity by educating others and delegating responsibilities across your chapter, other engineering chapters, and Group IT teams. Experience with Terraform, and platform solutions. Experience working on solutions with integrations between GCP and Azure. Knowledge of Cloud native, microservices and containerised systems. To have a strong desire for continuous improvement and an Agile way of working. Ideally in addition: Knowledge of the insurance and London Market ecosystem; Lloyd’s market experience is particularly valuable. Proven, hands-on software delivery experience, including platform engineering and/or build, release, and deployment engineering using modern DevOps practices. Experience delivering and operating technology in regulated environments, with a strong understanding of controls, audit expectations, and evidence-based compliance. Able to clearly explain the processes, patterns, and tooling used to ensure quality, stability, performance, scalability, secure deployment, maintainability, and effective documentation. Broad awareness of major cloud providers and services, with curiosity to evaluate and adopt capabilities that improve security, reliability, and cost efficiency. Proactive and improvement-focused, challenging the status quo and driving automation and simplification wherever it adds value. Strong delivery focus, able to prioritise effectively and deliver outcomes in a fast-paced environment with shifting demands. Able to operate effectively in a small, high-impact team while collaborating across a wider product/engineering organisation. Excellent communication and stakeholder-management skills, able to influence at all levels and present complex topics clearly. Comfortable working in ambiguity and adapting quickly as priorities, technology, and threats evolve. Up-to-date knowledge of security practices, processes, and tooling, with the judgement to apply emerging approaches pragmatically. Why Hiscox? This is a fantastic opportunity to join Hiscox during a time of focused growth where you will have the remit to make a real difference. At Hiscox we care about our people. We hire the best people for the job and we’re committed to diversity and creating a truly inclusive culture, which we believe drives success. Work with amazing people and be part of a unique culture Why work here? If you want to help build a brilliant future; work with amazing people; be part of a unique company culture; and, of course, enjoy great employee benefits that take care of your mental and physical wellbeing, come and join us. Get in touch If this is your first time visiting our career site and you wish to stay in touch please select the 'Introduce yourself' button on the top right. This will allow us to contact you with suitable vacancies. If you are a returning prospect and wish to view our current vacancies please Search for Jobs using the link on the top right. About us We’re a global, specialist insurer headquartered in Bermuda and listed on the London Stock Exchange. With 3,000 employees and 32 offices in 12 countries we’re a business with lots of opportunity for people with talent, spark and lots of ambition.
About Us: Solirius Reply, part of the Reply Group, is a technology consultancy and digital transformation partner that helps organisations solve complex challenges through strategy, design, engineering, and delivery. We work closely with our clients to deliver secure, accessible, user-focused services that evolve with their needs. By combining deep technical expertise with people-centred design, we create solutions that deliver meaningful, lasting impact. Our consultants partner directly with client teams, embedding into organisations to understand their goals, challenges, and users. This collaborative approach enables us to deliver tailored solutions that drive measurable outcomes across public and private sectors. Past and present clients include the Ministry of Justice, Department for Education, Ministry of Housing, Communities and Local Government, UEFA, International Olympic Committee, and Mercedes-Benz. Our services span the full digital delivery lifecycle, including architecture, engineering, delivery management, user-centred design, business analysis, data, DevOps, and AI. We operate as a collaborative and inclusive organisation that empowers our people to take ownership, innovate, and develop their expertise. As an equal opportunities employer, we are committed to encouraging equality, diversity, and social mobility, while creating opportunities for our teams to work on meaningful projects that deliver lasting impact. About You: You are a motivated and adaptable professional with a strong analytical mindset and a passion for using technology to solve real-world problems. You enjoy working in collaborative, agile teams and take pride in delivering high-quality solutions that make a tangible impact. With strong communication skills and a consultative approach, you’re comfortable engaging with clients, understanding their needs, and translating them into effective outcomes. The Role: We are seeking a highly skilled and motivated Security Cleared DevOps Engineer to join our team. The successful candidate will be responsible for designing, implementing, and maintaining secure, scalable, and automated infrastructure solutions across cloud and on-premises environments. This role requires an active security clearance and experience working within regulated or security-sensitive environments. You will work across AWS infrastructure, automation, networking, security, and DevOps, helping to build and maintain highly available, resilient, and compliant cloud platforms. The role is suited to an engineer who enjoys solving complex technical problems and working with modern cloud technologies in environments where security and reliability are critical. Requirements Key Responsibilities: Work with clients to understand technical requirements and translate them into robust AWS solutions. Design, build, migrate, and maintain secure and scalable AWS cloud environments. Deliver cloud engineering projects from initial design through implementation and transition into operations. Implement Infrastructure as Code using Terraform, CloudFormation, or similar technologies. Configure and manage AWS services including EC2, VPC, IAM, S3, RDS, Lambda, CloudWatch, Route 53, and Elastic Load Balancing. Design and implement secure AWS networking, including VPCs, subnets, routing, VPNs, security groups, and network controls. Develop automation and CI/CD pipelines to improve deployment speed, consistency, and reliability. Apply cloud security best practices, including least-privilege access, encryption, monitoring, logging, and secure configuration. Support cloud migrations, infrastructure modernisation, and application transformation programmes. Troubleshoot complex technical issues and provide clear recommendations to clients. Produce technical documentation, solution designs, implementation plans, and operational procedures. Work collaboratively with architects, developers, DevOps engineers, security specialists, and client stakeholders. Contribute to technical proposals, estimates, and solution development where required. Share knowledge and contribute to internal engineering standards, reusable solutions, and best practices. Maintain a strong understanding of emerging AWS technologies and cloud engineering practices. Key Skills/Experience: Proven commercial experience as an AWS Cloud Engineer, DevOps Engineer, Infrastructure Engineer, or similar. Strong hands-on experience with AWS infrastructure and cloud services. Experience delivering technical solutions within a consulting, systems integration, managed services, or professional services environment. Strong understanding of AWS networking, security, identity, and infrastructure architecture. Practical experience with Terraform, CloudFormation, or other Infrastructure as Code technologies. Experience with CI/CD and DevOps tooling. Strong Linux and/or Windows administration skills. Experience with scripting and automation using Python, Bash, PowerShell, or similar. Good understanding of cloud security principles and secure-by-design practices. Excellent problem-solving and troubleshooting skills. Strong communication skills with the ability to explain technical concepts to clients and stakeholders. Comfortable working across multiple projects, teams, and client environments. Active UK Security Clearance (SC or DV) or eligibility to obtain the required level of clearance. Desirable Skills AWS certification such as Solutions Architect, DevOps Engineer, SysOps Administrator, or Security Specialty. Experience with Kubernetes, Amazon EKS, Docker, or containerised platforms. Experience with Jenkins, GitHub Actions, GitLab CI, Azure DevOps, or similar CI/CD platforms. Ideally you will have coding experience with either Python or Javascript Experience delivering cloud migration and transformation programmes. Experience working with UK Government, Defence, National Security, or other highly regulated clients. Familiarity with security frameworks, accreditation, governance, and compliance requirements. Experience producing client-facing technical documentation and solution designs. Previous experience working in an Agile delivery environment. Benefits Competitive Salary Bonus Scheme Private Healthcare Insurance 25 Days Annual Leave + Bank Holidays Up to 10 days allocated for development training per year Enhanced Parental Leave Paid Fertility Leave (5 Days) Contributory Pension EAP with Help@Hand Gym Membership Benefits Flexible Benefits Allowance Cycle to Work and Electric Vehicle schemes Flexible Working Annual Away Days/Company Socials Diversity and Inclusion As an equal opportunities employer, we are committed to creating a work environment that supports, celebrates, encourages and respects all individuals, where all processes are based on merit, competence and business needs. Encouraging high social mobility is really important to us. We foster an inclusive culture by welcoming different perspectives, enabling equitable opportunities and promoting open dialogue. This commitment is reflected in initiatives such as our gender diversity group and our focus on mental health and wellbeing. Whatever stage you are at, you will find an environment where you can thrive. Should you require further assistance or require any reasonable adjustments to be put in place to better support your application process, please do not hesitate to raise this with us. As a Disability Confident employer, we are committed to ensuring our recruitment process is accessible and inclusive, enabling all candidates to demonstrate their skills, experience and potential.
TL;DR: We’re looking for a deeply technical Application Security Engineer to embed inside engineering and help secure Cloudsmith 2.0, the operating system for the modern software supply chain. The ideal person is a software engineer at heart who chose to specialize in security. You should be comfortable moving between code, architecture, and security design. About Cloudsmith Cloudsmith is building the operating system for the modern software supply chain. We run a global, fully managed, multi-tenant SaaS platform that helps organizations, from startups to the Fortune 500, secure, govern, and distribute software artifacts at scale. Worldwide, our customers use Cloudsmith as a critical infrastructure control plane for CI/CD, developer workflows, security controls, compliance, and software distribution, supporting 30+ formats and ecosystems across languages, containers, and operating systems. We recently raised our Series C to accelerate Cloudsmith 2.0: deeper artifact intelligence, stronger policy and provenance, faster package-aware delivery, and infrastructure built for engineering teams, as well as the modern AI-driven software factory. By developers, for developers: we care about craft, architecture, and enterprise scale. The Role As a Senior Application Security Engineer, you’ll report to the Head of Security and embed directly into one of our engineering tribes. You’ll work alongside Engineering Managers, Product Managers, Principal Engineers, and product engineers as part of the tribe’s day-to-day rhythm. Your job is to advocate for security from within the core engineering function, not from the sidelines. That means joining design discussions early, reviewing code and architecture, identifying risks early, and helping the tribe land secure, pragmatic fixes. We are building a model where security engineers are part-IC, part-security specialist. You should be able to contribute directly, but your greater leverage lies in raising the security judgment of the engineers around you, so good security becomes part of how we work. Key Responsibilities Embed inside an engineering tribe and participate in planning, design review, code review, incident learning, and delivery conversations. Collaborate across security, platform, and engineering guilds so security work routes to the right team, at the right time, with the right priority. Threat-model product and platform changes across APIs, workers, data stores, queues, object storage, CDNs, identity, policy, and tenant boundaries. Review production code and architecture for authentication, authorization, data access, secrets handling, artifact integrity, signing, auditability, and abuse cases. Build and improve security tooling, paved roads, checks, libraries, and automation that make securing Cloudsmith easier for engineers. Tune and operate security controls across SAST, DAST, SCA, secrets scanning, container scanning, IaC scanning, dependency analysis, and runtime signals. Investigate, triage, and remediate vulnerabilities identified through internal testing, third-party testing, responsible disclosure, customer reports, and security tooling. Support security incidents, red/blue exercises, detection work, and post-incident actions, improvements, and other investigatory/preventative follow-ups. Support technical control work for SOC 2, ISO 27001, EU CRA, and related frameworks, working with GRC where security engineering input is needed. Raise the tribe's security capability by helping engineers understand risks, threat-model their own work, and recognize what good secure design looks like. Required Experience, Qualities & Skills Technical Depth Around 5+ years of hands-on application security experience, or equivalent experience across software engineering and security, with security as your recent focus. Deep software engineering craft, with a focus on Python. Familiarity with TypeScript, Go, or Rust is an advantage. Effective use of ownership-driven AI is useful. Deep web and API security knowledge: OWASP Top 10, business logic flaws, authn/authz design, token handling, REST, GraphQL, and multi-tenant access control. Practical threat modeling and vulnerability research experience against real applications, APIs, cloud-native systems, and distributed services. Strong cloud-native security experience, especially across AWS, IAM, KMS, S3, containers, Terraform, CI/CD, secrets handling, logging, and multi-tenant isolation. Sound judgment on vulnerability priority. You understand CVSS, but you care more about exploitability, reachability, tenant impact, and production reality. Ability to reason through production systems: APIs, queues, caches, databases, workers, CDNs, object storage, edge delivery, telemetry, and failure modes. Clear communication in a remote-first environment. Your threat models, risk write-ups, incident notes, and feedback should be useful to engineers and credible to leadership. Software Supply Chain & Security Cloudsmith is not just another SaaS product. We are the artifact control plane for our customers’ software supply chains. You should understand, or be excited to go deep on: Ecosystems such as npm, PyPI, Docker/OCI, Maven, Helm, and Hugging Face. Software supply chain threats such as dependency confusion, typosquatting, malicious packages, maintainer compromise, metadata poisoning, and build-system injection. Artifact and registry concepts: immutable blobs, mutable metadata, package identity, checksums, upstream proxying, private repos, access control, caching, and promotion. Provenance and trust mechanisms such as SBOMs, signing, attestations, SLSA, Sigstore, in-toto, trusted publishing, and zero-trust software delivery. Bonus Points Experience securing artifact management, package registry, container registry, CI/CD, DevOps, developer tooling, or supply chain security platforms. Experience with secure runtime environments, sandboxing, workload isolation, policy engines, OPA/Rego, eBPF, or similar control points. Contributions to open-source security tooling or supply chain security projects. Familiarity with Datadog, AWS Security Hub, Okta, GitHub Advanced Security, Snyk, Semgrep, Trivy, Wiz, or similar tooling. Useful, but not required: certs such as OSCP, CSSLP, GPEN, GWAPT, GCSA, or CISSP. Cultural Values We're Looking For Engineering-first security: You operate as an engineer first for security problems. Builder mindset: You fix code and automate the boring parts to accelerate others. Practical paranoia: You can think like an attacker without losing sight of practicality. High standards, low ego: You raise the bar without devolving into arguments. Clear thinking: You can turn messy problems into decisions and trade-offs. Ownership: You care deeply about the security of the product, platform, and company. Impact & Growth This role helps shape application security for a platform that secures the software supply chain for organizations from startups to the Fortune 500. AI is increasing the rate at which software is created, changed, assembled, and shipped. Enterprises need stronger controls, better provenance, clearer trust decisions, and a faster path to delivery. Cloudsmith is building the critical infrastructure to record, govern, and deliver software artifacts at scale. You’ll help make that infrastructure safer from the inside. As the function grows, you’ll have the opportunity to shape our application security roadmap, define how security engineers embed within tribes, influence secure engineering patterns, mentor future security hires, and represent Cloudsmith externally in the security community. Benefits, Location & Work Environment You must be based in Ireland or the United Kingdom and have the right to work independently without requiring sponsorship. Headlines A position based in Ireland or the United Kingdom. A competitive compensation package, including equity. With comprehensive health, dental, and vision insurance. Plus, generous annual leave and flexible working policies to suit your lifestyle. Including a professional development budget for conferences and training. In a dynamic, innovative, trust-centric, and supportive work environment. Belfast HQ, used for working sessions, planning, all-hands, and team events. Opportunity to help shape a fast-growing company building critical infrastructure. Regular travel may be required for team meetings, planning, customers, and events. Health and Wellness We care about the health and wellness of our people and their families. Sustainable pace matters. We offer generous annual leave, health and wellbeing benefits, and flexible family-friendly working policies. Personal Growth You will have room to grow alongside strong colleagues. We support professional development through budgets for equipment, training, books, conferences, travel, and certifications. Facilities Cloudsmith is headquartered in Belfast, Northern Ireland, with fully equipped office space for working sessions, planning, meetups, and team activities. We rely on Slack, Google Docs, Linear, and other tools to collaborate across locations. About Equal Opportunity Cloudsmith is an equal-opportunity employer, proud to nurture a diverse workplace that welcomes applications from individuals of all races, genders, and ethnicities. We do not discriminate based on age, religion, sexual orientation, citizenship status, military service, or health conditions. We will not tolerate discrimination of any kind.
Browse UK visa sponsorship jobs.
By role
- Software engineering · 203
- DevOps and cloud · 35
- Data and AI · 24
- Cyber security · 6
- Engineering · 11
- Product and design · 7
By place
- London · 146
- Manchester · 17
- Birmingham · 5
- Bristol · 28
- Cambridge · 9
- Edinburgh · 13
- Glasgow · 6
- Belfast · 3
- Nottingham · 9
- Newcastle · 9
- Remote · 17
By employer
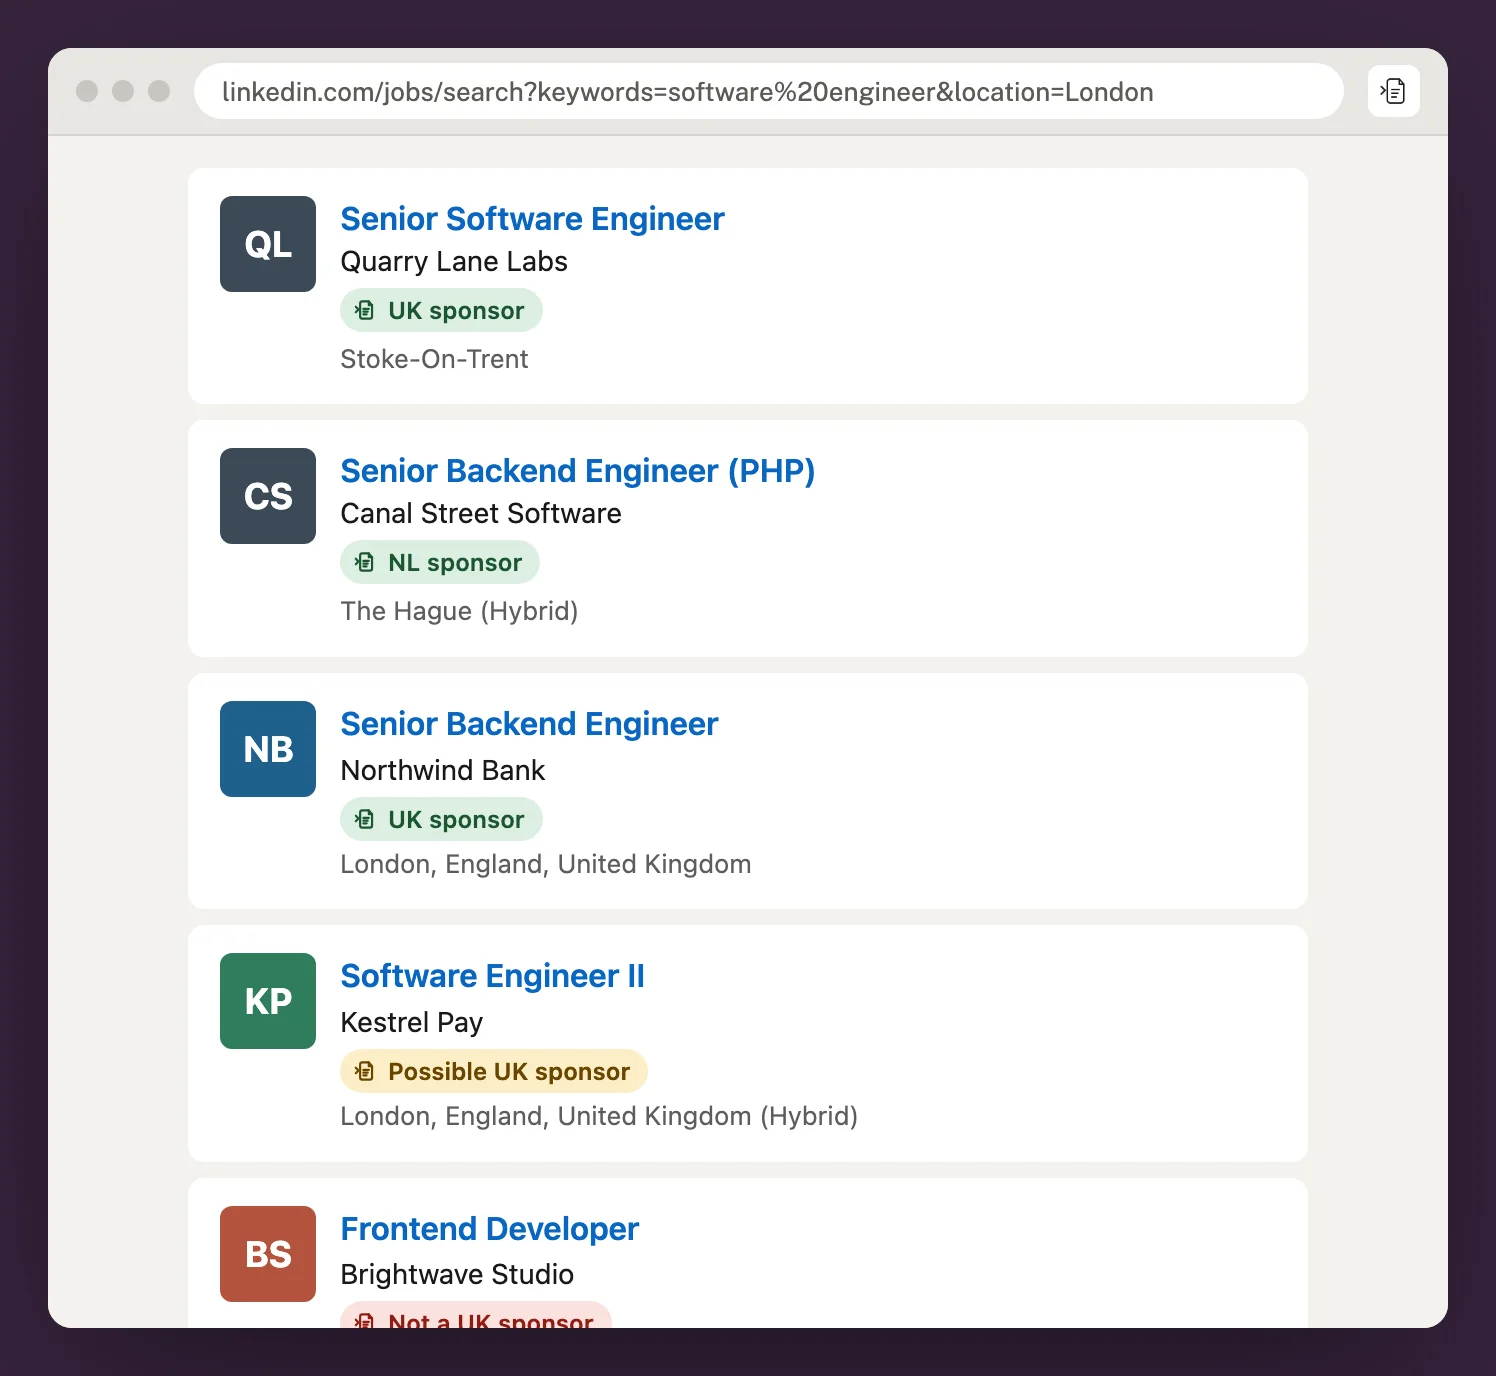
Chrome extension
Check sponsors while you browse LinkedIn.
Sponsor badges appear under every employer in LinkedIn, Indeed and Glassdoor search results, so you can see who can sponsor a visa before you open the job.